We accidentally leaked our Gemini API keys. Yep… not our proudest moment.
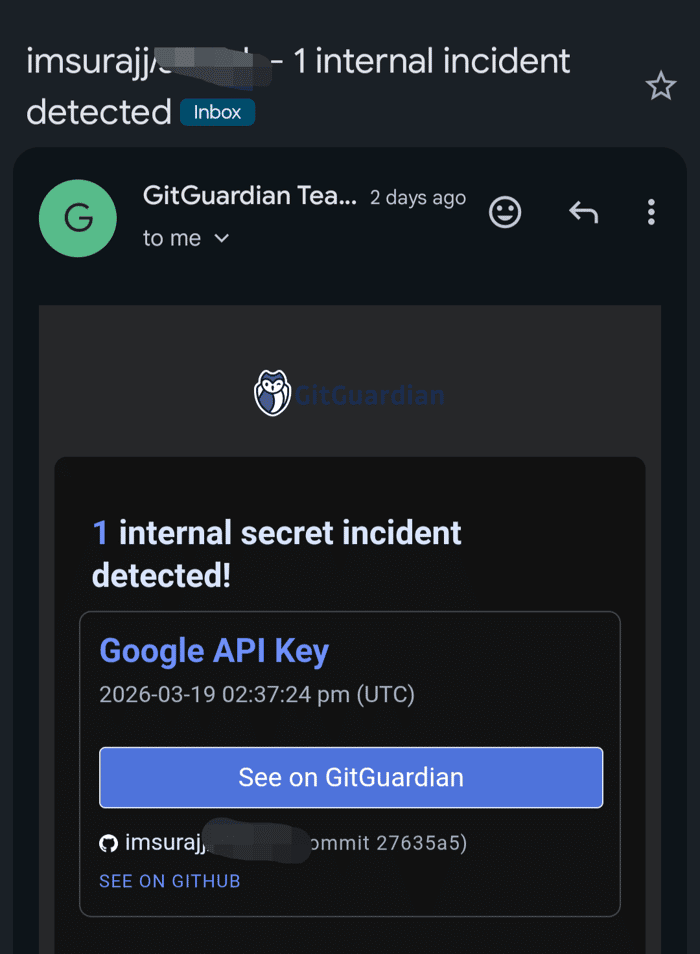
We accidentally leaked our Gemini API keys. Yep… not our proudest moment.
It wasn’t some crazy hack.
Just a simple mistake → pushed code without double-checking.
And that’s all it takes.
Within minutes, it could’ve turned into:
• Unexpected API bills 💸
• Abuse of our system
• Security risks we didn’t sign up for
Luckily, we caught it early.
Here’s what went down (and what you should steal from this):
1. Always check before pushing code
Sounds basic. Still ignored it.
.env files exist for a reason — use them.
2. If you leak it → revoke it immediately
Don’t “fix later.”
The longer it stays active, the more expensive it gets.
3. Use tools like GitGuardian
This literally saved us.
It alerted us before things got worse.
4. Never trust “it’s just a small test key”
There’s no such thing.
Every key = potential liability.
5. Set usage limits & alerts
Even if something leaks, damage should be capped.
6. Don’t add billing until you’re production-ready
If there’s no billing attached, worst case = limited damage.
Attach billing only when you're actually going live.
7. Separate environments (dev / prod)
Don’t let one mistake destroy everything.
8. As a founder, small mistakes = big costs
This isn’t just a dev issue.
It’s a business risk.
One leak at the wrong time can:
• Burn cash
• Break trust
• Kill momentum
We got lucky.
Next time, we don’t rely on luck.
👉 Curious about have you ever leaked an API key or secrets by mistake?
Or what’s your setup to prevent this?
Drop your story (or tools) below 👇
